
Firewalls
next-gen security at every perimeter
Next-generation firewalls and UTM appliances for the edge, the branch, and the data center — threat prevention from small sites to core throughput.
NGFW
Deep inspection
IPS/AV
Threat prevention
HA
Active/active pairs
The firewall brands we source
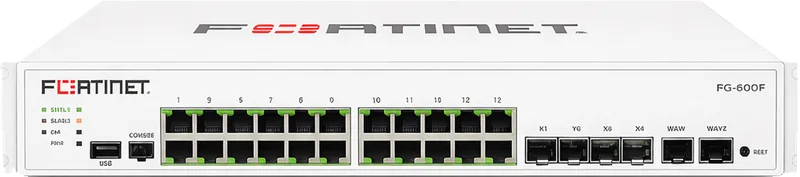

FortiGate next-gen firewalls from desktop to hyperscale, with FortiGuard threat services.
FortiGate 40F100F600F3000F
- Security chips (SPU) keep inspection fast
- SD-WAN built in at no extra cost
Threats stopped at every layer
L1
Application Control
Identify and police traffic by application, user, and content — not just ports.
L2
Threat Prevention
Integrated IPS, anti-malware, and sandboxing against known and zero-day threats.
L3
Encrypted Inspection
TLS/SSL inspection to see threats hiding in encrypted traffic.
L4
Secure SD-WAN
Routing, VPN, and security converged for the distributed edge.
Appliances for every site size
Small site
Branch / Desktop
Compact appliances securing small and remote sites.
Campus
Enterprise Edge
Perimeter firewalls with full threat-prevention throughput.
Core
Data-Center
High-throughput, low-latency appliances and HA clusters.
Perimeter & internet-edge securityBranch consolidation with secure SD-WANData-center segmentationRemote-access & site-to-site VPN